Maintainer of this skill?
by bighadj22
The open-source, COD-first e-commerce + delivery platform for Algeria built agentic-ready.
# Add to your Claude Code skills
git clone https://github.com/bighadj22/codflowLast scanned: 9/5/2026
{
  "issues": [
    {
      "type": "npm-audit",
      "message": "@esbuild-kit/core-utils: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@esbuild-kit/esm-loader: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@miniflare/cache: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@miniflare/core: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@miniflare/d1: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@miniflare/durable-objects: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@miniflare/html-rewriter: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@miniflare/r2: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@miniflare/shared-test-environment: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@miniflare/web-sockets: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@playform/compress: Vulnerability found",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "@playform/pipe: Vulnerability found",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "deepmerge-ts: DeepmergeTS has stack exhaustion when merging recursive object graphs",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "drizzle-kit: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "esbuild: esbuild enables any website to send any requests to the development server and read the response",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "fast-uri: fast-uri vulnerable to host confusion via skipped IDN canonicalization on scheme-relative references",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "miniflare: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "qs: qs array-limit bypass via bracket-key comma parsing",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "undici: Use of Insufficiently Random Values in undici",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "vitest-environment-miniflare: Vulnerability found",
      "severity": "medium"
    },
    {
      "file": ".agents/skills/codflow-setup/SKILL.md",
      "line": 280,
      "type": "secret-exfiltration",
      "message": "Instruction appears to send credentials/secrets to an external endpoint",
      "severity": "medium"
    },
    {
      "file": ".opencode/skills/codflow-setup/SKILL.md",
      "line": 280,
      "type": "secret-exfiltration",
      "message": "Instruction appears to send credentials/secrets to an external endpoint",
      "severity": "medium"
    }
  ],
  "status": "WARNING",
  "scannedAt": "2026-09-05T08:04:55.358Z",
  "npmAuditRan": true,
  "pipAuditRan": true,
  "promptInjectionRan": true
}See how codflow compares with popular alternatives.
codflow is an open-source ai agents skill for AI coding assistants such as Claude Code, Codex CLI, and ChatGPT, built by bighadj22. The open-source, COD-first e-commerce + delivery platform for Algeria built agentic-ready. It has 373 GitHub stars.
codflow returned warnings in SkillsLLM's automated security scan. It has no critical vulnerabilities, but review the flagged issues in the Security Report section before adding it to your workflow.
Clone the repository with "git clone https://github.com/bighadj22/codflow" and add it to your Claude Code skills directory (see the Installation section above).
codflow is primarily written in TypeScript. It is open-source under bighadj22 on GitHub, so you can review or fork the full source.
Yes. SkillsLLM lists many other AI Agents skills you can browse and compare side by side. Open the AI Agents category from the badge at the top of this page, or use the Related Skills and comparison links further down to weigh codflow against similar tools.
No comments yet. Be the first to share your thoughts!
Requires a passing catalog security scan.
⚠️ Third-Party Software Notice
This skill is third-party open-source software developed and hosted independently on GitHub. SkillsLLM is an informational directory and does not control or maintain the underlying repository.
Any security checks, ratings, or warnings displayed by SkillsLLM are automated and limited in scope. They do not constitute a security certification or guarantee that the software is safe, error-free, or free from malicious code, vulnerabilities, compromised dependencies, or prompt-injection risks.
Review the source code, permissions, dependencies, and configuration before installing or running any third-party skill. Use is at your own risk. To the maximum extent permitted by applicable law, SkillsLLM is not liable for losses arising from third-party software.

The open-source, COD-first e-commerce platform for Algeria — built agentic-ready.
Cash on Delivery meets serverless infrastructure. Self-host your entire commerce stack on Cloudflare with zero transaction fees, connect to Algeria's delivery carriers, and optimize Meta ads for real deliveries instead of door refusals.
Choose your path:
See it in action and deploy your own store.
→ See It in Action
→ What works today
→ Quick setup guide
→ Production deployment
Build features or customize CodFlow.
→ Contributing guide
→ Architecture overview
→ AI agent instructions
Watch the step-by-step setup guide:
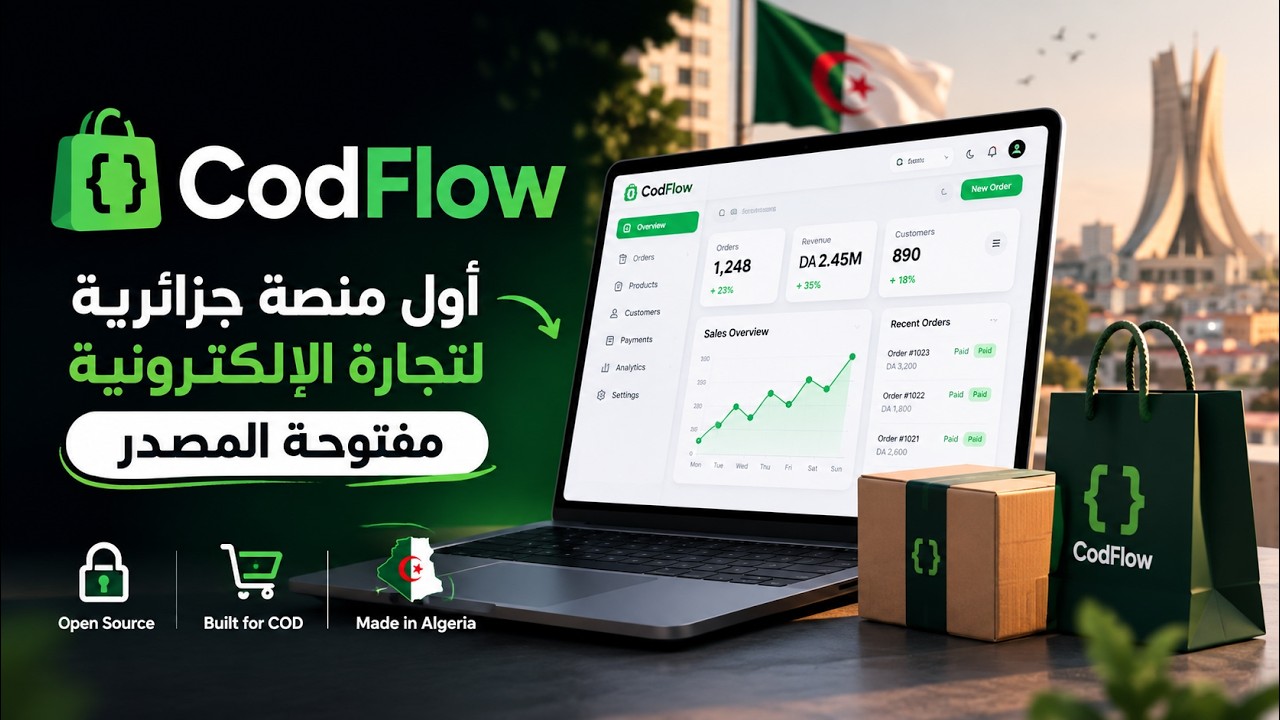
▶️ Watch: CodFlow Setup & Deployment Guide
E-commerce in Algeria is 95%+ Cash on Delivery (الدفع عند الاستلام). Western platforms like Shopify and local tools charge per-transaction fees, require expensive VPS hosting, and lock your data in their databases.
CodFlow is the first and only open-source COD e-commerce platform built for Algeria.
| The Reality | Western/Local Platforms | CodFlow |
|---|---|---|
| Transaction fees eat margins | 2–5% per order + monthly SaaS fees | $0 transaction fees — pay only Cloudflare hosting ($0–$5/mo) |
| Your data locked in their system | Can't export, can't migrate, vendor lock-in | You own everything — D1 database, R2 images, full control |
| Expensive hosting | VPS servers, maintenance, scaling costs | Serverless Cloudflare — auto-scales, zero maintenance |
| 4+ carrier portals | Juggle Yalidine, ZR, NOEST, EcoTrack separately | Unified carrier API — one integration for all carriers |
| In-house drivers ignored | No native driver dispatch or per-wilaya pay | Built-in driver management with compensation and cash settlement |
| Ads optimize for form fills, not deliveries | Meta Pixel fires on checkout submit (30–50% refuse at door) | Meta CAPI fires at actual delivery — optimize ads for real buyers |
Deploy CodFlow to your own Cloudflare account in minutes. No monthly fees. No transaction cuts. 100% open-source (Apache 2.0).
CodFlow v1.1.0 — here's what works today:
cod-astro/theme01)/lp/[slug]) — one-product marketing pages: stacked image story + COD form, no nav chrome/pages/[slug]) — Terms, Privacy, Refund/Return, Shipping (pre-seeded, merchant-editable) and any custom page, with a checkout consent line linking to themcod-client-astro)Lead at order placement or Purchase at confirmed deliverytest_event_code)fbp, fbc sent unhashed as requiredfbp and fbc attribution preservationcapi_event_log) for every send attemptcod-server)/api/docsKnown Limitations:
See docs/KNOWN_LIMITATIONS.md for honest coverage of incomplete features and platform constraints.
Run CodFlow locally in 5 steps:
🤖 Using an AI Coding Assistant? CodFlow includes an autonomous setup skill. Tell your agent: "Set up CodFlow" and it will follow the
codflow-setuprunbook.
Already set up and want the latest version? Don't redo the setup. Tell your agent: "Update CodFlow" — it will follow the codflow-update runbook, which pulls the latest code from this repository's main branch, applies new database migrations, keeps your resources, secrets, and store data intact, rebuilds and redeploys your workers, and reports each step in plain language.
npm install -g wranglergit clone https://github.com/bighadj22/codflow.git
cd codflow
npm ci
Names are yours to choose — scripts read them from the root .env
(see step 3), so nothing is hardcoded.
wrangler login
wrangler d1 create my-codflow-db
wrangler r2 bucket create my-codflow-images
wrangler kv namespace create RATE_LIMIT
wrangler kv namespace create OAUTH_KV
# Repo root — resource names for the seeders, the D1 wrapper, the R2 CORS
# setup and the storefront deploy helper. Precedence: process.env > .env > default.
cp .env.example .env
# Set COD_ACCOUNT_ID, COD_DB_NAME, COD_R2_BUCKET_NAME, COD_SERVER_URL, COD_MEDIA_DOMAIN

# Backend
cd cod-server
cp .dev.vars.example .dev.vars
cp wrangler.toml.example wrangler.toml
# Update wrangler.toml with your D1 database_id, R2 bucket_name, KV ids

# Dashboard
cd ../cod-client-astro
cp wrangler.toml.example wrangler.toml   # same D1 database_id as cod-server + your KV id
cp .env.example .env
cp .dev.vars.example .dev.vars
# Set BETTER_AUTH_SECRET (same value as cod-server's, e.g. openssl rand -hex 32)

# Storefront
cd ../cod-astro/theme01
cp .dev.vars.example .dev.vars
cd cod-server
npm run db:setup:local

cd ../cod-client-astro
ADMIN_EMAIL=admin@example.com ADMIN_NAME=Admin npm run seed:admin
# ⚠️ Save the generated password and API key
Open three terminals:
# Terminal 1: Backend (http://localhost:8787)
cd cod-server && npm run dev

#