Maintainer of this skill?
by QwenLM
An open-source AI coding agent that lives in your terminal.
# Add to your Claude Code skills
git clone https://github.com/QwenLM/qwen-codeGuides for using ai agents skills like qwen-code.
Last scanned: 8/4/2026
{
  "issues": [
    {
      "type": "npm-audit",
      "message": "@babel/core: @babel/core: Arbitrary File Read via sourceMappingURL Comment",
      "severity": "low"
    },
    {
      "type": "npm-audit",
      "message": "@hono/node-server: Node.js Adapter for Hono: Path traversal in `serve-static` on Windows via encoded backslash (`%5C`)",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@isaacs/brace-expansion: @isaacs/brace-expansion has Uncontrolled Resource Consumption",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "@larksuiteoapi/node-sdk: Vulnerability found",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "@microsoft/api-extractor: Vulnerability found",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "@microsoft/api-extractor-model: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@microsoft/tsdoc-config: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@mobilewright/core: Vulnerability found",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "@modelcontextprotocol/sdk: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@opentelemetry/core: OpenTelemetry Core: Unbounded memory allocation in W3C Baggage propagation",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@opentelemetry/exporter-logs-otlp-grpc: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@opentelemetry/exporter-logs-otlp-http: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@opentelemetry/exporter-logs-otlp-proto: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@opentelemetry/exporter-metrics-otlp-grpc: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@opentelemetry/exporter-metrics-otlp-http: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@opentelemetry/exporter-metrics-otlp-proto: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@opentelemetry/exporter-prometheus: Vulnerability found",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "@opentelemetry/exporter-trace-otlp-grpc: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@opentelemetry/exporter-trace-otlp-http: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@opentelemetry/exporter-trace-otlp-proto: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@opentelemetry/exporter-zipkin: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@opentelemetry/instrumentation-http: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@opentelemetry/otlp-exporter-base: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@opentelemetry/otlp-grpc-exporter-base: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@opentelemetry/otlp-transformer: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@opentelemetry/propagator-b3: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@opentelemetry/propagator-jaeger: Vulnerability found",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "@opentelemetry/resources: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@opentelemetry/sdk-logs: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@opentelemetry/sdk-metrics: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@opentelemetry/sdk-node: Vulnerability found",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "@opentelemetry/sdk-trace-base: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@opentelemetry/sdk-trace-node: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@rushstack/node-core-library: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@rushstack/terminal: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@rushstack/ts-command-line: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "@vitest/browser: Vitest Browser: Exposed Browser Mode API Can Proxy CDP and Overwrite Config Files, Leading to RCE",
      "severity": "critical"
    },
    {
      "type": "npm-audit",
      "message": "@vitest/coverage-v8: Vulnerability found",
      "severity": "critical"
    },
    {
      "type": "npm-audit",
      "message": "ajv: ajv has ReDoS when using `$data` option",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "axios: Axios has a NO_PROXY Hostname Normalization Bypass that Leads to SSRF",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "brace-expansion: brace-expansion: Zero-step sequence causes process hang and memory exhaustion",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "diff: jsdiff has a Denial of Service vulnerability in parsePatch and applyPatch",
      "severity": "low"
    },
    {
      "type": "npm-audit",
      "message": "dompurify: DOMPurify: `CUSTOM_ELEMENT_HANDLING` bypasses `afterSanitizeElements` for allowed custom elements.",
      "severity": "low"
    },
    {
      "type": "npm-audit",
      "message": "echarts: Apache ECharts has a cross-site scripting (XSS) vulnerability",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "esbuild: esbuild enables any website to send any requests to the development server and read the response",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "fast-uri: fast-uri vulnerable to host confusion via backslash authority introducer",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "flatted: flatted vulnerable to unbounded recursion DoS in parse() revive phase",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "hono: Hono: ReDoS in CORS middleware via Access-Control-Request-Headers",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "ip-address: ip-address: Address4 decodes leading-zero octets as decimal while resolvers decode them as octal, allowing SSRF and trust-boundary bypass",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "js-yaml: JS-YAML: Quadratic-complexity DoS in merge key handling via repeated aliases",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "linkify-it: linkify-it: Quadratic-complexity DoS via the `mailto:` validator scan-loop on attacker text",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "lodash: lodash vulnerable to Code Injection via `_.template` imports key names",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "minimatch: minimatch has a ReDoS via repeated wildcards with non-matching literal in pattern",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "mobilewright: Vulnerability found",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "picomatch: Picomatch: Method Injection in POSIX Character Classes causes incorrect Glob Matching",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "postcss: PostCSS has XSS via Unescaped </style> in its CSS Stringify Output",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "protobufjs: protobufjs: Denial of Service via infinite loop in .proto option parsing",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "rollup: Rollup 4 has Arbitrary File Write via Path Traversal",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "sharp: sharp inherited vulnerabilities in libvips: CVE-2026-33327, CVE-2026-33328, CVE-2026-35590, CVE-2026-35591",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "storybook: Storybook Dev Server is Vulnerable to WebSocket Hijacking",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "tar: node-tar: Uncontrolled recursion in mapHas/filesFilter allows uncatchable stack-overflow DoS via crafted long-path tar with member selection",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "undici: undici vulnerable to TLS certificate validation bypass via dropped requestTls in SOCKS5 ProxyAgent",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "uuid: uuid: Missing buffer bounds check in v3/v5/v6 when buf is provided",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "vite: Vite middleware may serve files starting with the same name with the public directory",
      "severity": "high"
    },
    {
      "type": "npm-audit",
      "message": "vite-node: Vulnerability found",
      "severity": "medium"
    },
    {
      "type": "npm-audit",
      "message": "vitest: Vulnerability found",
      "severity": "critical"
    }
  ],
  "status": "FAILED",
  "scannedAt": "2026-08-04T06:27:15.466Z",
  "npmAuditRan": true,
  "pipAuditRan": true,
  "promptInjectionRan": true
}See how qwen-code compares with popular alternatives.
qwen-code is an open-source ai agents skill for AI coding assistants such as Claude Code, Codex CLI, and ChatGPT, built by QwenLM. An open-source AI coding agent that lives in your terminal. It has 28,878 GitHub stars.
qwen-code failed SkillsLLM's automated security scan, which flagged one or more high-severity issues. Review the Security Report section carefully before using it.
Clone the repository with "git clone https://github.com/QwenLM/qwen-code" and add it to your Claude Code skills directory (see the Installation section above).
qwen-code is primarily written in TypeScript. It is open-source under QwenLM on GitHub, so you can review or fork the full source.
Yes. SkillsLLM lists many other AI Agents skills you can browse and compare side by side. Open the AI Agents category from the badge at the top of this page, or use the Related Skills and comparison links further down to weigh qwen-code against similar tools.
No comments yet. Be the first to share your thoughts!
Based on votes and bookmarks from developers who liked this skill
Requires a passing catalog security scan.
⚠️ Third-Party Software Notice
This skill is third-party open-source software developed and hosted independently on GitHub. SkillsLLM is an informational directory and does not control or maintain the underlying repository.
Any security checks, ratings, or warnings displayed by SkillsLLM are automated and limited in scope. They do not constitute a security certification or guarantee that the software is safe, error-free, or free from malicious code, vulnerabilities, compromised dependencies, or prompt-injection risks.
Review the source code, permissions, dependencies, and configuration before installing or running any third-party skill. Use is at your own risk. To the maximum extent permitted by applicable law, SkillsLLM is not liable for losses arising from third-party software.


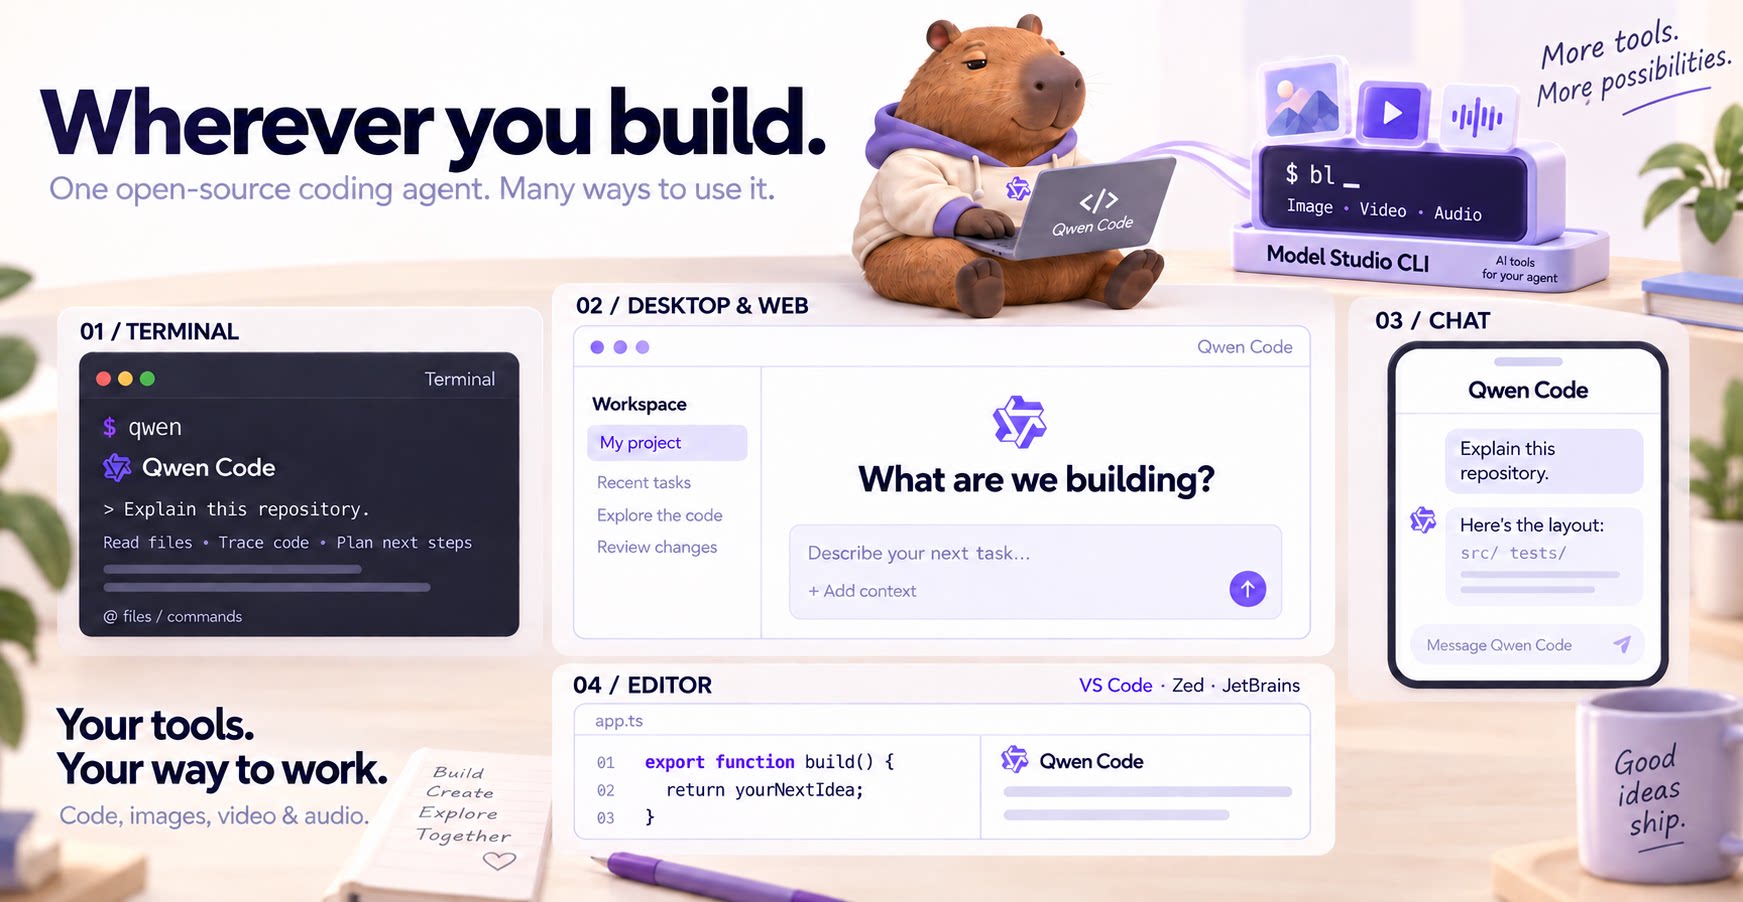
The open-source AI coding agent for your terminal, editor, desktop, browser, and chat.
中文 | Deutsch | français | 日本語 | Русский | Português (Brasil) | 한국어
[!TIP] Qwen Code is actively iterating on itself — using its own agent and models to file issues, submit PRs, review code, and run tests. Powered by the community, driven by AI.
Linux / macOS:
curl -fsSL https://qwen-code-assets.oss-cn-hangzhou.aliyuncs.com/installation/install-qwen-standalone.sh | bash
Windows:
irm https://qwen-code-assets.oss-cn-hangzhou.aliyuncs.com/installation/install-qwen-standalone.ps1 | iex
Restart your terminal after installation to ensure environment variables take effect.
NPM (requires Node.js 22+):
npm install -g @qwen-code/qwen-code@latest
Homebrew (macOS / Linux):
brew install qwen-code
Open a terminal in your project and start Qwen Code:
cd /path/to/your-project
qwen
Inside the session, run /auth to configure your provider and API key. Then try:
Explain this repository and show me where to start.
See the Authentication Guide and Settings Reference for detailed setup.

Choose the interface that fits your workflow:
| Interface | Get started |
|---|---|
| Terminal | Run qwen in your project — see Quick Start. |
| Desktop | Download Qwen Code Desktop for macOS, Windows, and Linux. |
| Web | Run qwen serve --open to open the Web UI in your browser. (experimental) |
| Editor | Set up VS Code, Zed, or JetBrains. |
| Chat | Connect Telegram, DingTalk, WeChat, or Feishu, then run qwen channel start. |
For automation and custom integrations:
qwen -p "..." in scripts, CI/CD, or batch jobs.qwen serve to connect clients over HTTP + SSE (ACP). (experimental) Daemon guide.import asyncio
from qwen_code_sdk import is_sdk_result_message, query
async def main() -> None:
result = query(
"Summarize the repository layout.",
{
"cwd": "/path/to/project",
"path_to_qwen_executable": "qwen",
},
)
async for message in result:
if is_sdk_result_message(message):
print(message["result"])
asyncio.run(main())
Run Qwen Code as a long-lived service when you want browser, editor, SDK, and automation clients to share agent sessions without each starting a separate process. The daemon provides the built-in Web Shell and an HTTP + SSE API, supports multiple workspaces, and lets clients reconnect to active sessions.
Start it in the foreground and open the Web Shell:
qwen serve --open
The default address is http://127.0.0.1:4170. To run and manage it in the background instead:
qwen daemon start
qwen daemon status
qwen daemon logs -f
qwen daemon stop
By default, the daemon listens on loopback without bearer authentication; any local process that can reach it can use the full API, including code execution. On shared or untrusted hosts, set QWEN_SERVER_TOKEN and use --require-auth. See the Daemon guide for workspaces, authentication, remote access, and the API.
If you know Claude Code, you already know Qwen Code — and then some. We've put significant effort into bringing Qwen Code to feature parity with Claude Code, improving both breadth and reliability across the board.
| Feature | Qwen Code | Claude Code |
|---|---|---|
| SubAgents, Agent Teams, Dynamic Workflows | ✓ | ✓ |
| Auto-Memory, Auto-Skills, Hooks | ✓ | ✓ |
| Built-in Skills (/review, /batch, /loop, /bugfix…) | ✓ | ✓ |
| MCP, Plan Mode, LSP Integration | ✓ | ✓ |
| Auto Mode, Sandbox, Git Worktrees | ✓ | ✓ |
| Computer Use (desktop automation) | ✓ | ✓ |
| IDE Plugins (VS Code / JetBrains / Zed) | ✓ | ✓ |
| SDK | ✓ | ✓ |
| Hea |